

Administration officials discuss cybersecurity threats affecting hospitals, health care sector
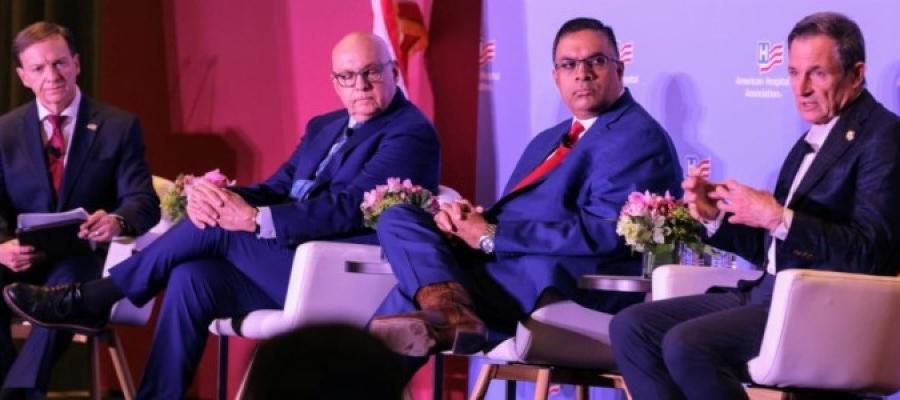
Two Administration officials April 14 discussed how the federal government is working with hospitals and other parts of the health care sector to defend against cyber threats and mitigate cyberattacks.
Anne Neuberger, deputy assistant to the president and deputy national security advisor for cyber and emerging technology on the National Security Council, spoke about how the Department of Health and Human Services, Cybersecurity and Infrastructure Security Agency, and other federal agencies are working to share timely information related to cyber threats with health care providers.
In a conversation with AHA National Advisor for Cybersecurity and Risk John Riggi, Neuberger spoke about voluntary consensus-based cybersecurity practices that were announced in January by HHS as part of the Administration’s efforts to bolster cybersecurity. These cybersecurity performance goals, which the AHA helped develop and supports, are targeted at defending against the most common tactics used by cyber adversaries to attack health care and related third parties.
The AHA opposes insufficiently funded proposals for mandatory cybersecurity requirements that carry excessively harsh penalties being levied on hospitals. Instead, AHA is urging Congress and the Administration to focus on the entire health care sector and not just hospitals to make meaningful progress in the war on cybercrime.
In a separate panel discussion, CISA Deputy Director Nitin Natarajan talked about how the cyber threat landscape continues to evolve and how all parts of the health care sector are facing increased threats.
The panel also included J. Stephen Jones, M.D., president and CEO of Inova Health System, and Brian Gragnolati, president and CEO of Atlantic Health System, who shared strategies that their organizations are implementing to strengthen cybersecurity efforts and protect patient safety.