

Sen. Mark Warner urges nation to put cybersecurity first in fight to protect sensitive data
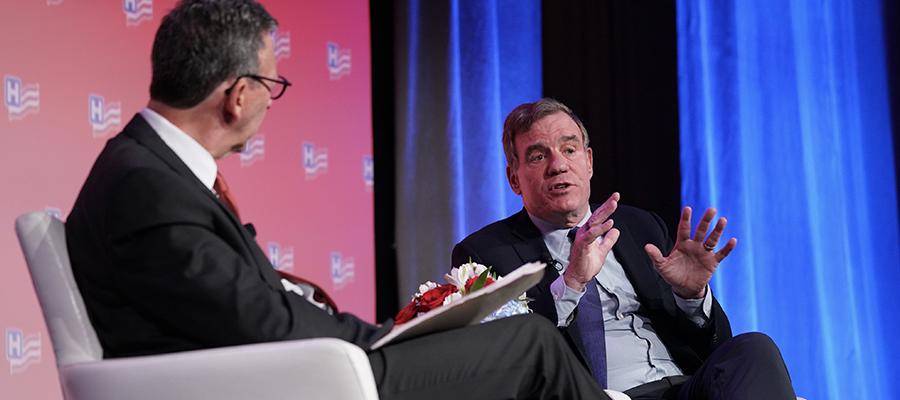
More than 1,000 executive leaders from the nation’s top hospitals and health systems convened at the 2023 AHA Annual Membership Meeting, April 23-25 in Washington, D.C.
Health care cybersecurity has too often been an afterthought, with protections added after an internal review or external attack discover a vulnerability, Sen. Mark Warner, D-Va., told moderator former CNN Washington bureau chief Frank Sesno at today’s federal plenary session.
Warner called for a clearer chain of command at the federal level when it comes to health care cyber policy; a “bill of sale” to make medical device software more visible to patients and providers; and minimum mandatory cybersecurity standards for the health care field.
“I don’t think you can just say ‘another unfunded mandate,’” Warner said about the costs of building a stronger cybersecurity shield for health care. “But we’ve put up with a lot of technology where some firms, frankly, put out vulnerable product on an ongoing basis.”
Putting cybersecurity first, rather than looking at it as tool to use after a system has been compromised, is the best way to protect sensitive data, he said. “It’s like washing your hands before you go into the OR. Otherwise, you find it’s the weakest link in the chain where the bad guys can get in.”
For more on the 2023 AHA Annual Meeting, read AHA's coverage.